ISO Certifications | Compliance Services | Data Security | Risk Management | Audit & Consulting & ISO Certifications | Compliance Services | Data Security | Risk Management | Audit & Consulting
About Us
Surkshanow is a global consulting firm specializing in compliance and management system consulting services. We help businesses strengthen security, achieve regulatory compliance, and build operational excellence through standards such as SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, and other international frameworks. With a client-focused approach and industry expertise, we support organizations in building secure, compliant, and future-ready businesses.
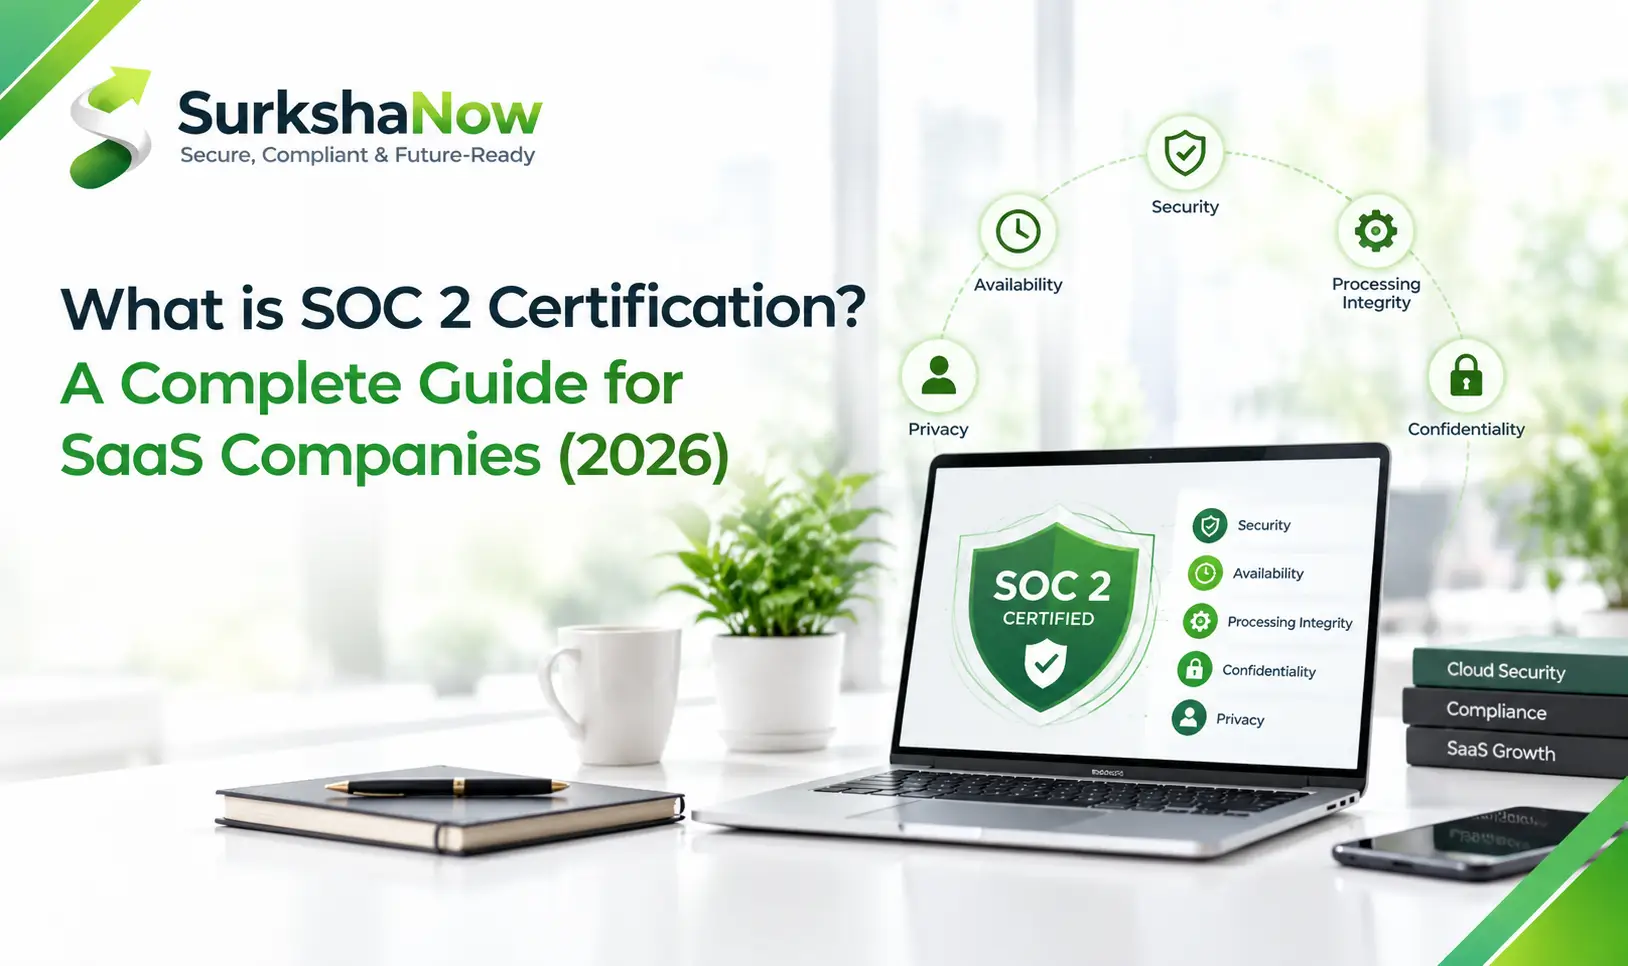
What is SOC 2 Certification? A Complete Guide for SaaS Companies (2026)
Introduction
As cyber threats grow and more businesses use cloud-based apps, customers expect their data to be safe. For SaaS companies and tech service providers, showing strong security is now essential. It protects sensitive information, builds trust, and helps win enterprise clients.
This is where SOC 2 Certification comes in.
SOC 2 is a well-known security standard for organizations that handle customer data. Whether you are a startup aiming for enterprise sales or a growing SaaS company entering new markets, getting SOC 2 compliant can boost your credibility.
This guide covers everything you need to know about SOC 2 certification—its benefits, process, timeline, costs, and how SurkshaNow can help your company get ready for an audit.
What is SOC 2 Compliance?
SOC 2 (System and Organization Control 2) is a voluntary security framework established by the American Institute of Certified Public Accountants (AICPA). It defines how cloud-based service providers must manage, protect, and handle customer data.
Technically, there is no such thing as a "SOC 2 Certificate." Unlike ISO 27001, which gives you a formal certificate, SOC 2 provides an Attestation Report from an independent, licensed CPA (Certified Public Accountant) firm.
Unlike rigid, prescriptive compliance standards that force you to buy specific software, SOC 2 is principle-based. It asks a simple question: Does your organization have controls that are designed to effectively mitigate security risks for your specific architecture?
Here is that section reformatted as a clear, scannable list instead of a table:
The 5 Trust Services Criteria (TSC) Explained
Your SOC 2 audit is measured against five Trust Services Criteria. You do not need all five; instead, you customize your audit scope based on your product and customer promises.
Security (Common Criteria): This is the foundational pillar and the only mandatory criterion for every SOC 2 audit. It evaluates whether your systems are protected against unauthorized access, focusing on your firewalls, access controls, multi-factor authentication (MFA), encryption, and continuous threat detection.
Availability: Focuses on whether your systems remain accessible for operation and use as promised. It evaluates system uptime, disaster recovery plans, redundancy, and network performance monitoring. This is essential if you provide infrastructure tools, hosting services, or promise strict SLAs (like 99.9%+ uptime) to your customers.
Confidentiality: Ensures that sensitive corporate data—such as intellectual property, internal financial records, or proprietary business plans—is protected and restricted to authorized personnel. You will need this if your B2B platform stores, processes, or shares sensitive business documents and trade secrets.
Processing Integrity: Guarantees that your system's data processing is complete, valid, accurate, and timely. If you operate a fintech app, payment gateway, e-commerce engine, or a data transformation tool, this criterion proves to your customers that your system doesn't drop, duplicate, or improperly alter data during transactions.
Privacy: Dedicated to how your system collects, uses, retains, and discloses Personally Identifiable Information (PII). While Confidentiality focuses on corporate data, Privacy focuses on protecting individual end-user data from misuse. You should include this if your application handles consumer data or healthcare information, or if you need to align with data privacy frameworks such as GDPR.
SOC 2 Type 1 vs. Type 2: What’s the Difference?
When starting your journey, you will choose between two types of SOC 2 reports. Most SaaS companies start with Type 1 before progressing to Type 2.
Feature
SOC 2 Type 1
SOC 2 Type 2
What it tests
Design of your security controls at a single point in time.
Operational effectiveness of controls over a period.
Observation Window
None (Snapshot on a specific date).
3 to 12 months (typically 6 months).
Time to Complete
Fast (usually 2 to 3 weeks).
Requires waiting out the observation window.
Enterprise Value
Unlocks early conversations; proves intent.
Gold Standard required to close major enterprise deals.
The 5-Step Roadmap to Becoming SOC 2 Audit-Ready
Getting certified does not have to mean months of engineering downtime or endless spreadsheets. Here is the proven path SaaS teams use:
1.Define Scope & Select Criteria
Determine which cloud environments (AWS, GCP, Azure), repositories, and application services fall into the audit boundary. Select Security plus any relevant criteria like Availability or Confidentiality.
2.Perform Gap Analysis & Risk Assessment
Map your current setup against AICPA controls. Identify gaps—such as missing multi-factor authentication (MFA) on legacy tools, unencrypted backup storage, or missing background check records.
3.Remediate & Automate Policies
Fix technical gaps and publish core security policies (Access Control, Incident Response, Change Management). Enforce technical controls like mandatory SSO/MFA, centralized SIEM logging, and vulnerability scanning.
4.Gather Evidence & Run Observation Window
For Type 2, continuous evidence is key. Instead of taking manual screenshots of access lists or deployment approvals, connect automated tooling to continuously record logs, PR approvals, and backup checks.
5.Execute CPA Audit & Share Report
An independent CPA auditor reviews your control evidence, tests sample populations, conducts brief staff interviews, and issues your final SOC 2 Attestation Report.
Why Choose SurkshaNow for SOC 2 Certification?
Achieving SOC 2 used to mean months of manual labor, endless spreadsheets, hiring expensive consultants, and taking engineers away from building your product. SurkshaNow changes that.
Here is why fast-growing startups and enterprises trust SurkshaNow:
80% Faster Audit Readiness: Our platform automates evidence collection by connecting directly to your tech stack (AWS, GitHub, Google Workspace, Jira, Okta, and more).
Auditor-Approved Policy Templates: Don't waste time drafting security policies from scratch. Use our pre-built, auditor-backed templates customized to your infrastructure.
Real-Time Automated Monitoring: SOC 2 Type 2 requires continuous compliance. SurkshaNow monitors your environment 24/7 and alerts you the moment a control drifts out of compliance.
End-to-End Expert Guidance: You don't have to figure out complex AICPA frameworks alone. Our compliance experts guide you through scoping, gap remediation, and auditor hand-off.
Transparent & Founder-Friendly Pricing: Get top-level compliance automation without high enterprise costs. Our pricing is made to help startups grow without breaking the bank.
Benefits of SOC 2 Certification for SaaS Growth
Getting SOC 2 compliant isn't just about passing a security test—it is a strategic growth lever for modern software companies. Here is what achieving SOC 2 unlocks for your business:
Unlocks Enterprise Deals: Large enterprise buyers won't even evaluate software without a SOC 2 report. Getting compliant lets you pitch to Fortune 500 companies with confidence.
Builds Immediate Market Trust: Displaying your commitment to security positions your brand as a mature, trustworthy player—even if you are an early-stage startup.
Hardens Security Architecture: The compliance process helps you identify hidden vulnerabilities, enforce access controls, and prevent costly data breaches before they occur.
Gives You a Competitive Edge: When competing against rivals with similar feature sets, having SOC 2 compliance often becomes the single deciding factor for buyers.
Fast-Track Your SOC 2 Compliance with SurkshaNow
Do not let long security questionnaires and manual evidence collection slow down your sales. SurkshaNow automates your SOC 2 process from the start by connecting to your cloud, code repositories, and HR tools to keep you always ready for audits.
Zero Spreadsheet Hassle: 100+ automated integrations collect evidence in the background.
Auditor-Approved: Pre-built security policy templates built for modern cloud setups.
Unblock Enterprise Deals: Get audit-ready for Type 1 in weeks.
1. Is SOC 2 certification mandatory for SaaS companies?
Legally, no. SOC 2 is a voluntary compliance standard. But in practice, it is almost required if you sell B2B software to enterprise, US-based, or security-focused clients. Most enterprise procurement teams will not sign a contract without a current SOC 2 report.
2. How long does it take to get SOC 2 compliant?
With traditional manual methods, preparing for a SOC 2 audit takes 3 to 6 months of heavy engineering effort. With SurkshaNow’s automated evidence collection and policy templates, most SaaS teams achieve audit readiness for Type 1 in just weeks. For Type 2, the process moves into a 3- to 6-month observation window during which SurkshaNow continuously tracks your controls.
3. How much does a SOC 2 audit cost?
Total costs depend on your company’s size, technical setup, and the CPA auditor you pick. Traditional auditor fees are usually $15,000 to $40,000 or more, plus many hours of staff time. SurkshaNow cuts these internal costs by automating up to 80% of evidence collection and connecting you with trusted, startup-friendly auditors.
4. Can we jump straight to SOC 2 Type 2, or should we do Type 1 first?
Yes, you can go straight to Type 2. But if you have an urgent enterprise deal waiting, getting a SOC 2 Type 1 report first gives you quick proof of compliance in just a few weeks. Then you can move right into your Type 2 observation period without slowing down sales.
5. How long is a SOC 2 report valid for?
A SOC 2 report covers a set period in the past, usually 6 to 12 months for Type 2. Enterprise clients expect you to renew your report every 12 months to show your security is still strong.
Recent Insights
September 28, 2026
Master DPDP Act 2023 Compliance in India: The Complete Business Strategy
With the DPDP Rules notified, Indian businesses face strict compliance milestones leading to May 2027. Discover the phase-by-phase timeline, key requirements, and how SurkshaNow simplifies your DPDP Act implementation.
Ultimate DPDP Act 2023 Compliance Checklist for Indian Businesses
Get the ultimate DPDP Act 2023 compliance checklist for Indian businesses. Learn key requirements, avoid severe penalties, and automate data privacy now.
How to Choose the Right SOC 2 Compliance Consultant for Your Business
Choose the best SOC 2 compliance consultant for your SaaS or tech firm. Discover step-by-step selection tips and how to fast-track SOC 2 Type 1 & 2 readiness.
Essential cookies keep this website working. With your permission, analytics cookies help us understand page visits. Optional tracking stays off until you choose. Cookie policy · Privacy policy