SOC 2 Type II Certification in India: Main Challenges and Practical Solutions
Stop compliance stress before it starts. Learn how Indian tech businesses use automated SOC 2 Type II readiness to win international client trust.
Read More →
Today, enterprise buyers and B2B clients expect their vendors to take security seriously. A System and Organization Controls (SOC) 2 report is no longer just a bonus—it is now essential for doing business. If you run a SaaS platform, cloud infrastructure company, or managed service provider, getting SOC 2 compliant can help you win big deals, earn customer trust, and protect your company’s reputation.
However, going through the SOC 2 audit process can feel overwhelming. It takes technical know-how, a solid understanding of the AICPA Trust Services Criteria, and substantial internal resources.
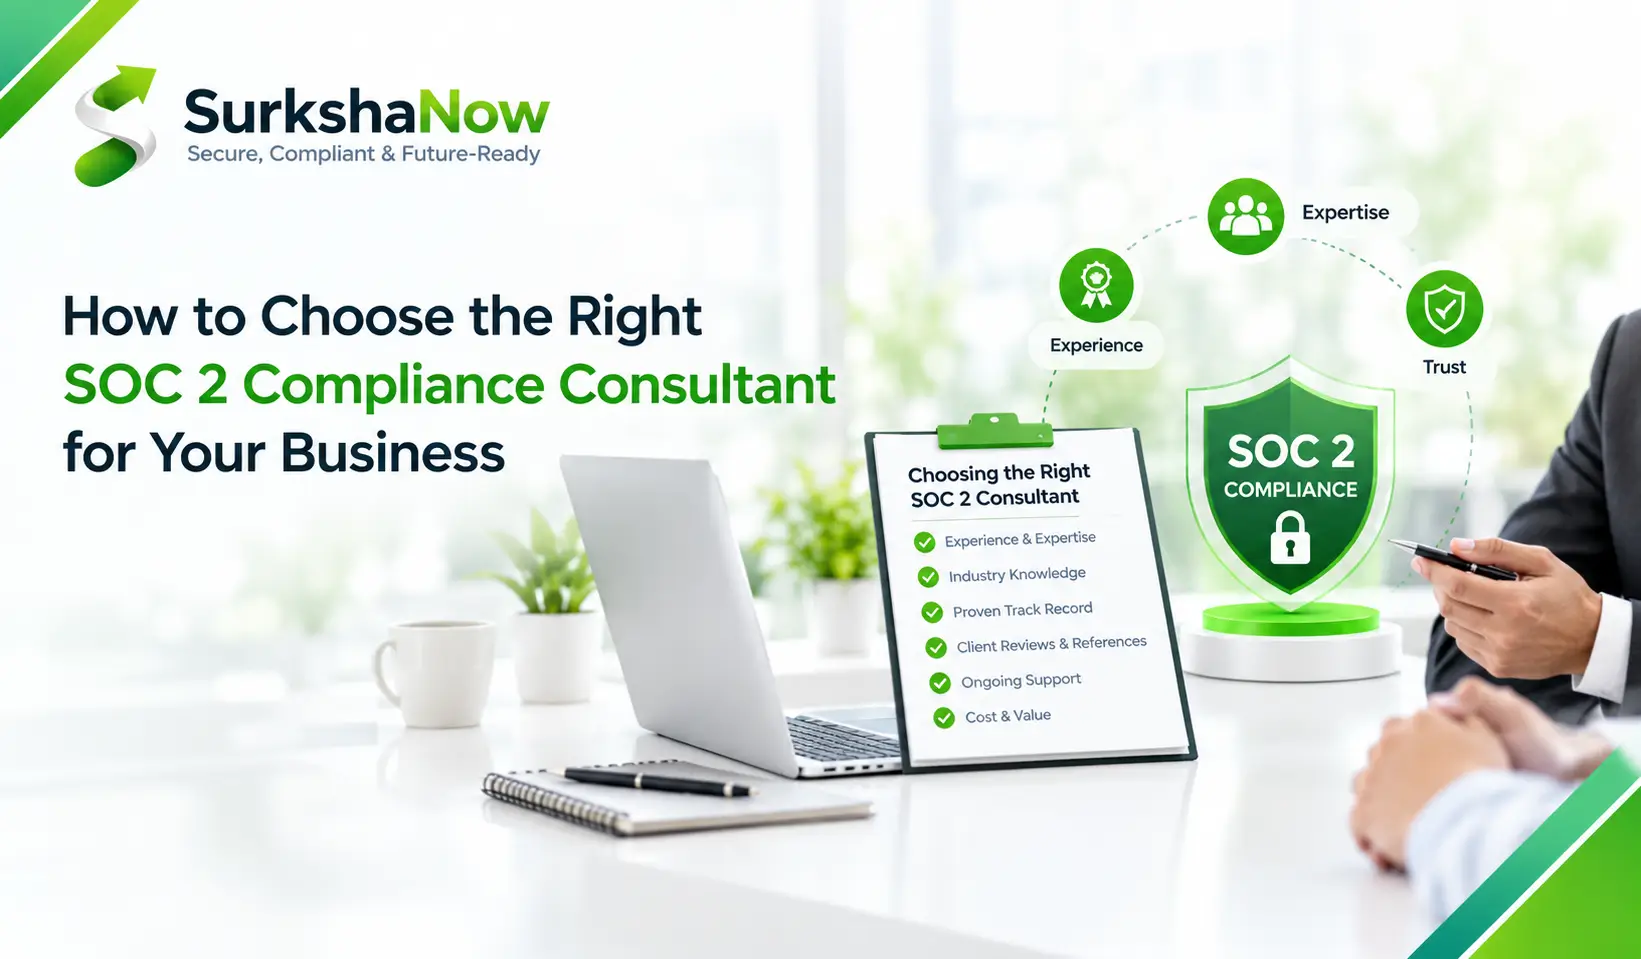
That’s why having expert help is so important. Choosing the wrong advisor can mean higher costs, missed deadlines, failed audits, and lost revenue. In this guide, we’ll show you how to choose right SOC 2 compliance consultant and how partners like SurkshaNow can help you get ready for SOC 2 quickly and smoothly.
A SOC 2 compliance consultant is your advisor throughout the compliance process. While only an independent CPA firm can conduct the audit and issue the SOC 2 report, a consultant prepares your organization for the audit before it even begins.
Trying to handle SOC 2 compliance on your own can lead to unexpected problems. Your engineering team might spend countless hours gathering evidence, writing documents, and trying to understand complex compliance terms instead of working on your main product.
Partnering with an experienced SOC 2 advisory service offers key benefits:
To select the best compliance partner for your company, evaluate prospective advisors using these seven essential criteria:
Compliance is not just about paperwork; it is also highly technical. Your advisor should really understand today’s cloud platforms (such as AWS, Azure, and Google Cloud), container systems (such as Docker and Kubernetes), CI/CD pipelines, and modern technology stacks.
Key Question to Ask: Does the consultant have direct experience evaluating security architectures similar to ours?
Understanding the difference between SOC 2 Type 1 and Type 2 reports is essential:
| Feature | SOC 2 Type 1 | SOC 2 Type 2 |
| Focus | Evaluates control design at a single point in time. | Evaluates control operational effectiveness over a period (3–12 months). |
| Speed | Fast (Ideal for closing immediate sales deals). | Comprehensive (Preferred by mature enterprise buyers). |
| Audit Duration | Single snapshot. | 3, 6, or 12-month monitoring window. |
A good consultant will help you through both stages. They can quickly get you a SOC 2 Type 1 report to meet urgent client needs while also preparing your controls for long-term SOC 2 Type 2 certification.
Collecting evidence by hand—like taking lots of screenshots, logging access reviews, and tracking policy signatures in spreadsheets—is slow and often leads to mistakes.
Look for consultants who leverage modern compliance automation technology. Automated tools continuously pull evidence from your tech stack (GitHub, AWS, Okta, Jira, HRIS), reducing manual effort by up to 80%.
Copying generic security policies from the internet can cause problems. If an auditor finds that your policies do not align with how your business actually operates, you could receive audit exceptions. Choose a consulting firm that tailors policies, workflows, and controls to your business.
Compliance costs can spiral out of control without clear boundaries. Watch out for traditional hourly billing models that encourage scope creep. Instead, look for consultants offering clear, fixed-fee packages that bundle gap remediation, policy creation, automated software integration, and audit support.
A consultant is not allowed to issue your final SOC 2 audit report; only an accredited, independent CPA firm can do that. Still, the best SOC 2 consultants have strong relationships with audit firms, which help make scheduling easier, lower fees, and smooth the process between advice and auditing.
SOC 2 is not a one-time project; it is something you need to do every year. Pick a partner who will help you keep your security strong, conduct yearly risk assessments, manage vendor checks, and handle yearly reassessments.
To protect your organization from bad actors or inexperienced advisors, watch out for these major red flags:
At SurkshaNow, we understand that B2B growth depends on trust, speed, and security. We bridge the gap between traditional enterprise compliance consulting and next-generation compliance automation software, helping companies achieve SOC 2 audit readiness up to 5x faster than traditional methods.
The Challenge: A growing B2B SaaS startup was on the verge of signing a major enterprise client contract worth $300,000 ARR. However, the enterprise security team required a SOC 2 Type 1 report within 60 days as a closing prerequisite. The startup lacked dedicated security personnel, formal policies, and automated controls.
The Solution: The company partnered with SurkshaNow.
The Result: The client received their SOC 2 Type 1 report in less than six weeks, signed the $300,000 contract, and set up ongoing monitoring to prepare for their annual SOC 2 Type 2 review.
Choosing the right SOC 2 compliance consultant is a key decision for your company. The best advisor will have technical cloud skills, clear pricing, hands-on help with policies, and automated tools for gathering evidence. This way, you can improve security without slowing your business down.
Do not let compliance issues slow down your sales or stop you from closing big deals. With SurkshaNow, you get expert security advisors, advanced automated readiness tools, and a clear path to fast, stress-free SOC 2 compliance.
Schedule a free SOC 2 strategy call with SurkshaNow today and find out how quickly your business can become audit-ready!
A SOC 2 consultant (like SurkshaNow) helps you prepare for compliance by identifying gaps, developing policies, implementing technical controls, and guiding evidence collection. A SOC 2 auditor must be an independent, CPA-accredited firm legally authorized to perform the official assessment and issue the final SOC 2 report.
The cost depends on company size, technical complexity, existing security controls, and the number of Trust Services Criteria included in the scope. On average, overall costs (consulting, technology tools, and CPA audit fees) range between $15,000 and $60,000+. Choosing a tech-enabled partner like SurkshaNow significantly lowers overall costs by streamlining readiness efforts.
Traditional manual methods usually take 6 to 12 months. With SurkshaNow’s tech-enabled approach and expert guidance, companies can complete readiness and achieve a SOC 2 Type 1 report in as little as 4 to 8 weeks. SOC 2 Type 2 requires an additional 3- to 12-month monitoring period.
Yes! In fact, early-stage startups often achieve SOC 2 compliance faster than large legacy enterprises because their cloud infrastructures are smaller, simpler, and easier to automate.
Security (Common Criteria) is mandatory for every SOC 2 report. Depending on your business model, SLA commitments, and customer contract demands, you can add Availability, Confidentiality, Processing Integrity, or Privacy. SurkshaNow helps you define the ideal audit scope during your initial onboarding.
Stop compliance stress before it starts. Learn how Indian tech businesses use automated SOC 2 Type II readiness to win international client trust.
Read More →Compare SOC 2 Type 1 vs Type 2 compliance. Learn key differences in timeline, cost, and requirements to choose the right report with SurkshaNow.
Read More →With the DPDP Rules notified, Indian businesses face strict compliance milestones leading to May 2027. Discover the phase-by-phase timeline, key requirements, and how SurkshaNow simplifies your DPDP Act implementation.
Read More →